Показаны сообщения с ярлыком Microsoft. Показать все сообщения

понедельник, 18 мая 2009 г.

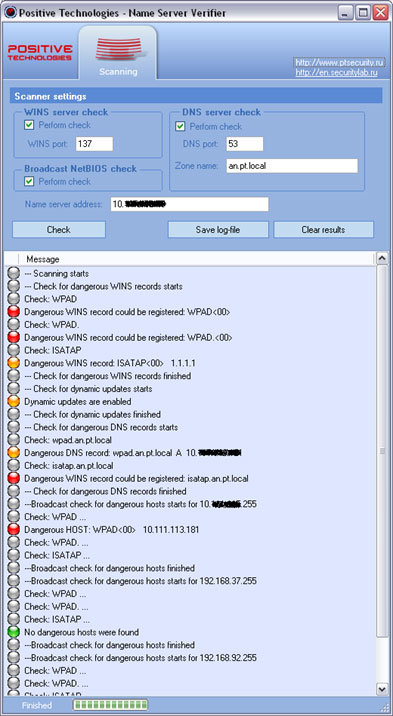
Tool for WINS and DNS (MS-09-008)

The utility is used to detect potentially dangerous entries in DNS and WINS services databases. The utility also allows local network scanning to detect hosts with dangerous NetBIOS names. If system administrators and security administrators use the utility regularly then it allows controlling potentially dangerous entries in name servers and availability of hosts with dangerous NetBIOS names in local network.


Detail information could be found in the article by Sergey Rublev and on SecurityLab:

http://www.securitylab.ru/news/extra/380522.php

http://www.securitylab.ru/_download/articles/wpad_weakness_en.pdf

Download here:
http://www.ptsecurity.ru/download/wpadcheck_en.zip

понедельник, 20 апреля 2009 г.

Microsoft has published regular Security Intelligence Report.

Russia is among leaders by infected computers percentage:
The infection metrics is about 21,1 for 1000 runs of "cleaner" , an world average index is 8,6. A very strange index.


It is possible that the index is strongly concerned with a possibility to infect different platforms:


I think nobody is surprised that a lot of home users with XP SP0, SP1 are afraid to update it because they are should that their cracked Windows versions will not further work. But will they have Malicious Software Removal Tool? Will a “master” bring on a floppy disk? Rather, something from Kaspersky or DrWeb.

This is a very strange situation. Can it really be corporate employees ?

PS. Actually this is a wonderful report.
The most common threat in Russia – Taterf which is spread through shared folders, in USA - Win32/Renos and Win32/Zlob. There are a lot data about Conficker in the report, but it is missed in statistics first lines.

Is it a wonder?
воскресенье, 12 апреля 2009 г.

Security in our life

I has taken a flight from Domodedovo airport (Moscow) recently, and thought a lot…
And my thoughts were hard… Hope, only in Britain and only on submarines.


PS. If somebody do not recognize – this is Symantec - Kido/Conficker/Downadup.

вторник, 24 февраля 2009 г.

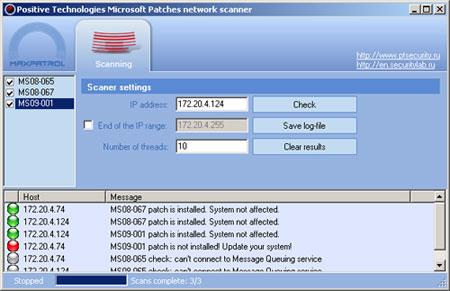
We’ve published a network utility to check that security updates from MS08-065, MS08-067 and MS09-001 are installed in the system. The utility does not need administration privileges and works in pentest mode.
Feedback on the previous releases was quite positive, we decided to upgrade.


Additional info:
http://www.securitylab.ru/news/extra/368760.php

Downloads:
http://www.ptsecurity.com/download/pt-check-09-001.zip

понедельник, 24 ноября 2008 г.

IE 8 and XSS

Here are the results of analysis of XSS filter built in current beta Internet Explorer 8. Colleagues from Microsoft have achieved rather good results – the most widespread attack vectors for the vulnerability are blocked.
If we take into account that XSS is the most widespread Web problem according to both Positive Technologies and international WASC statistics, the existence of such mechanisms in browsers is a useful initiative. I think Avir/HIPS developers should also care about this area.

There is a contracted summery below about filter efficiency against different attack vectors:

Stored version
No
DOM-Based
Partly
Reversed version
In tag
No
In Javascript
No
In HTML
Yes
In tag parameter
Yes

It is funny that the different vulnerability (HTTP Response Splitting) was detected that allows attackers to disable XSS protection. I hope the problem will be solved in the release version.